No Silos. No Interns.
Pure Adversarial Penetration.
[INFO]
Principal Operator & Executive Leadership
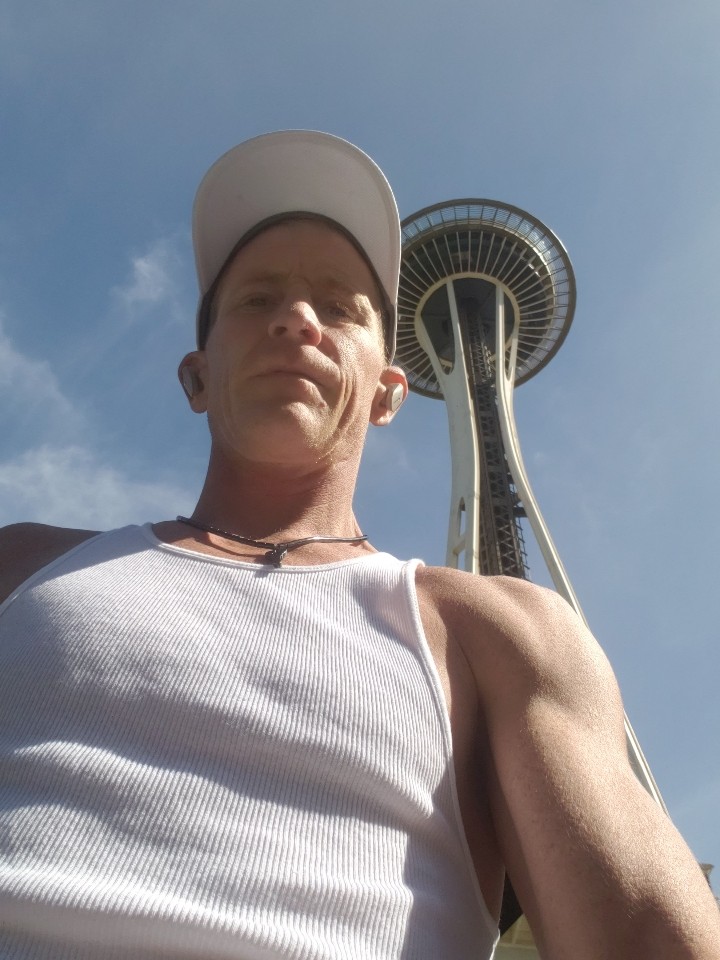
Founder & Chief Executive Officer
Lead Adversary & Physical Intrusion Specialist
01 // COMMAND DIRECTIVE
Adversaries don't follow ticketing workflows. Neither do I.
When enterprise cybersecurity teams hire global consulting giants, they often pay for senior partner credentials but get junior analysts executing automated, cookie-cutter scanners.
At Vortex Offensive Labs, you engage directly with me. As the owner, CEO, and sole operator, every line of shellcode, lock bypass, social engineering pretext, and debrief report is personally planned and executed with absolute precision, total discretion, and relentless tenacity.
Bypassing access control, RFID cloning, tailgating, and secure server room breaching.
Active directory compromise, EDR evasion, C2 payload execution, pivoting to critical assets.
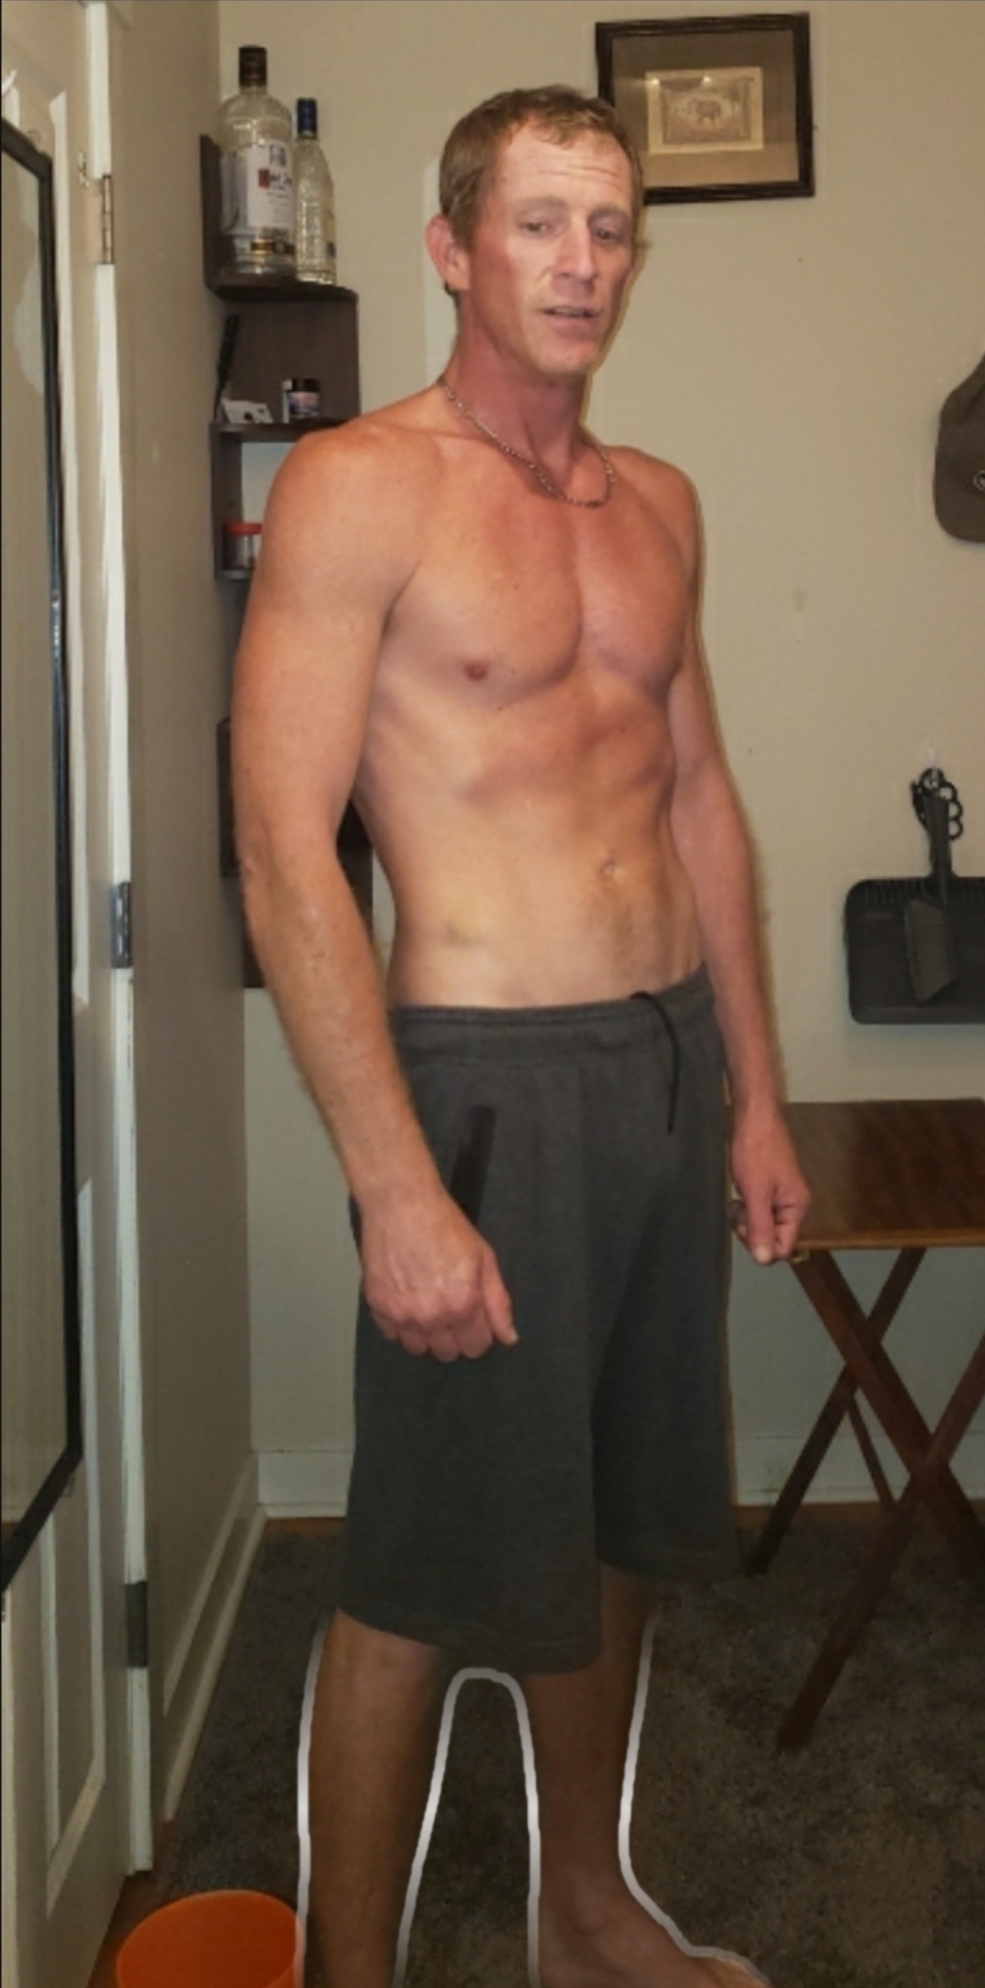
Red teaming isn't just digital. True threat actors scale fences, climb air ducts, and exploit perimeter physical lapses. I maintain peak operational fitness for rigorous field intrusions.
Why A Solo Principal Beats A Big Firm
Eliminating bureaucracy creates agility. Discover the operational superiority of contracting a dedicated offensive specialist.
Zero Communication Silos
In corporate security agencies, account managers relay sanitized notes between clients and analysts. Here, you debrief in real-time with the actual person inside your network or building.
Unbounded Adversarial Adaptability
Corporate consultancies are bound by rigid checklists and hourly project managers. I pivot on the fly—switching from phishing to physical cloning to zero-day logic chaining whenever a realistic opportunity emerges.
Strict Discretion & Integrity
Confidential exploit techniques, architecture maps, and executive vulnerabilities are never passed to an offshore tier-1 team. Sensitive intelligence stays locked in encrypted vaults accessible by one person only.
Full-Spectrum Capabilities
SIMULATING ADVANCED PERSISTENT THREATS (APT) // MITRE ATT&CK FRAMEWORK
Offensive Red Teaming
- › Custom C2 Infrastructure
- › Endpoint / EDR Evasion
- › Active Directory Escalation
- › Ransomware Path Mapping
Physical Intrusion Ops
- › RFID / NFC Badge Emulation
- › Lock-Picking & Bypass Tools
- › Under-Door & REX Exploitation
- › Rogue Hardware Plant (Dropbox)
Human Vector & OSINT
- › High-Conviction Spearphishing
- › In-Person Impersonation Pretext
- › Open-Source Reconnaissance
- › Telecom & Vishing Tactics
Executive Digital Sanitization
- › VIP Threat Exposure Audit
- › Public Footprint Scrubbing
- › Doxxing Vulnerability Assessment
- › Family Residence Perimeter Recon
Field Recon & Tactical Dossier
PHOTOGRAPHIC FIELD SURVEILLANCE • TARGET RECONNAISSANCE • ADVERSARIAL CULTURE
 RECON // SITREP
Urban OSINT & Perimeter Recon
Live field mapping in high-density environments, analyzing public egress, physical blind spots, and perimeter vulnerabilities.
 OPS // CULTURE
Unorthodox Infiltration Pretexts
Blending into urban landscapes requires thinking outside sterile manuals. Exploiting social blind spots through disarming, unconventional pretexts.
 EXECUTIVE // LIAISON
Executive Advisory & Debrief
Translating high-severity technical exploit chains into actionable remediation intelligence for boards, counsel, and executives.
 MASCOT // ATTITUDE
Unapologetic Adversary Mindset
We don't pull punches to preserve egos. True security resilience is forged when your systems survive genuine adversarial aggression.
Configure Your Engagement
Select target vectors for an instant tactical estimate and direct transmission to the Principal.